
Cryptographic & Physical Security
Engineered to Survive Compromised Credentials
Assume an attacker gains root access to your production database server. Nordic Data Sync ensures historical backups remain unreadable, undeletable, and forensically verifiable.
Defense-in-Depth Key Hierarchy
Every byte traverses three independent cryptographic layers from your host memory down to physical NAND/platter sectors.
-
1
Zero-Knowledge Client Cipher (SSE-C / Repo Key)
Tools like Restic, Kopia, and pgBackRest encrypt payloads with AES-256-GCM or ChaCha20-Poly1305 before transmission. Nordic Data Sync never sees plaintext keys.
-
2
Per-Bucket Envelope Wrapping via FIPS 140-3 HSM
Each object shard is wrapped again server-side with a unique ephemeral 256-bit DEK sealed by redundant PCIe HSMs in Stockholm and Helsinki.
-
3
Immutable WORM Clock Anchored to GNSS Stratum-1
Object Lock expiration timestamps are evaluated against hardware GPS/Galileo receivers inside our cages, neutralizing NTP spoofing attacks.
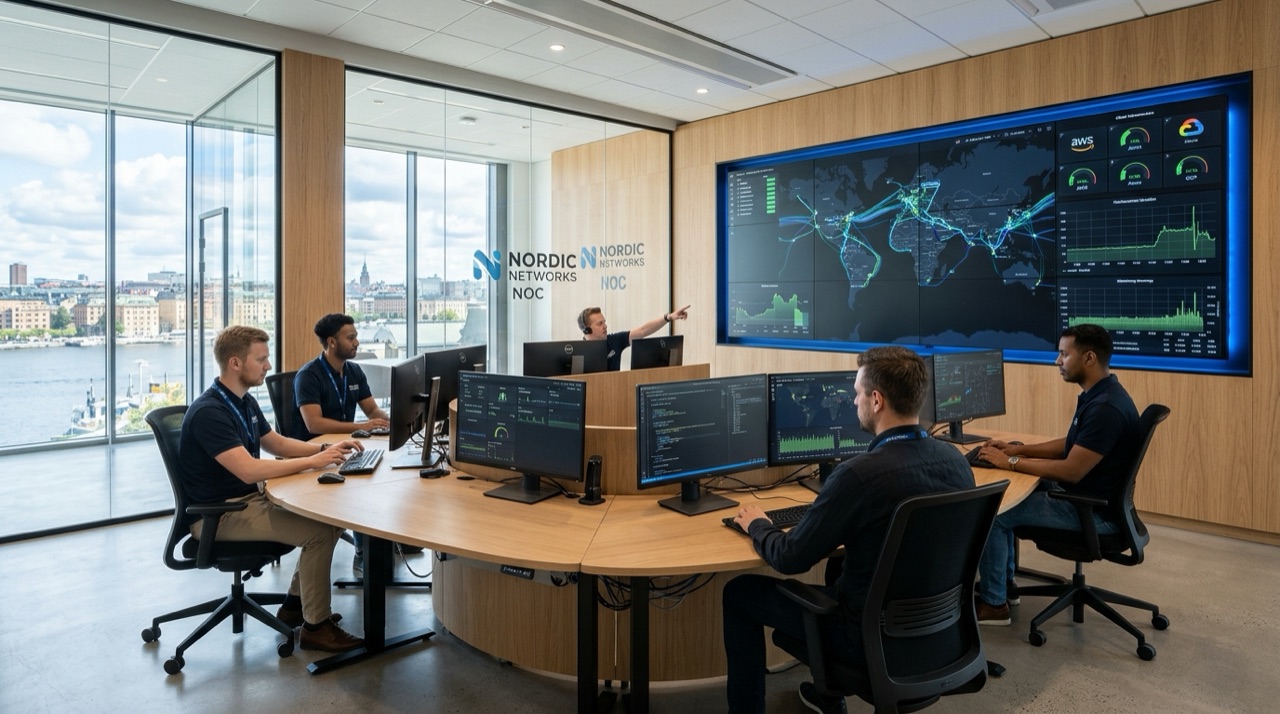
Continuous SIEM anomaly detection and hardware HSM quorum monitoring in Kista, Stockholm.
| Threat Scenario | Standard Cloud S3 Bucket | Nordic Data Sync (Compliance WORM + Scoped IAM) |
|---|---|---|
| Leaked CI/CD or Host S3 Key | Attacker runs s3 rm --recursive |
Blocked: Append-only IAM + ASN/IP allowlist rejects external IPs & deletes |
| Compromised Tenant Admin Console | Attacker shortens lifecycle policy to 1 day | Blocked: COMPLIANCE lock forbids lifecycle truncation even by root |
| Silent Storage Media Bit-Rot | Detected only when restore fails months later | Healed: 14-day SHA-256 Merkle scrubber reconstructs from RS(8+4) parity |
| Subpoena Under Foreign Extraterritorial Law | Subject to US CLOUD Act parent jurisdiction | Protected: 100% Swedish AB ownership + zero-knowledge client ciphertext |